



Cloud computing has changed how businesses, students, and organizations use technology. Instead of buying and managing physical servers, companies now rely on cloud platforms to store data, run applications, and deliver digital services. While this shift brings flexibility and cost savings, it also raises an important question: who is responsible for security in the cloud? This is where Cloud Security Basics and the shared responsibility model become essential to understand.
Many people believe that moving to the cloud means security is fully handled by the cloud provider. In reality, cloud security is a shared effort between the cloud service provider and the customer. The shared responsibility model explains how cloud security responsibilities are divided and why both sides play a critical role. Understanding this model helps prevent data breaches, compliance issues, and misconfigurations that often lead to security incidents.
This comprehensive guide explains the shared responsibility model in simple terms. It breaks down customer vs cloud provider security roles, explains cloud service provider security obligations, and highlights cloud customer security responsibilities. By the end, you will clearly understand how cloud security works and what steps are needed to stay protected.
Cloud Security at a Basic Level
Cloud security refers to the set of policies, technologies, controls, and practices designed to protect data, applications, and infrastructure hosted in the cloud. These protections ensure confidentiality, integrity, and availability of information.
At its core, cloud security focuses on protecting data from unauthorized access, preventing service disruptions, and meeting regulatory requirements. Unlike traditional on-premises systems, cloud environments are dynamic. Resources can be created, modified, or deleted in minutes. This flexibility makes security both more powerful and more complex.
Cloud Security Basics are built on the idea that security is not a single tool or feature. It is a continuous process that involves identity management, network protection, data encryption, monitoring, and compliance controls.
What Is the Shared Responsibility Model in Cloud Computing
The shared responsibility model in cloud computing defines how security duties are divided between the cloud provider and the customer. Instead of one party handling everything, both share responsibility for securing different layers of the cloud environment.
The cloud provider secures the underlying infrastructure that runs cloud services. This includes physical data centers, hardware, and foundational software. The customer, on the other hand, is responsible for securing what they put into the cloud, such as data, applications, and user access.
This model ensures that security responsibilities are clear. When customers understand their role, they can avoid common mistakes like leaving storage buckets public or failing to manage user permissions properly.
Why the Shared Responsibility Model Matters
The shared responsibility model matters because most cloud security failures are not caused by cloud providers. They are caused by customer misconfigurations, weak passwords, or lack of monitoring.
When organizations misunderstand cloud security responsibilities, they may assume certain protections are already in place when they are not. This false sense of security can lead to data leaks, ransomware attacks, and compliance violations.
By clearly defining customer vs cloud provider security roles, the shared responsibility model reduces confusion and helps organizations design stronger security strategies.
Cloud Service Models and Security Responsibilities
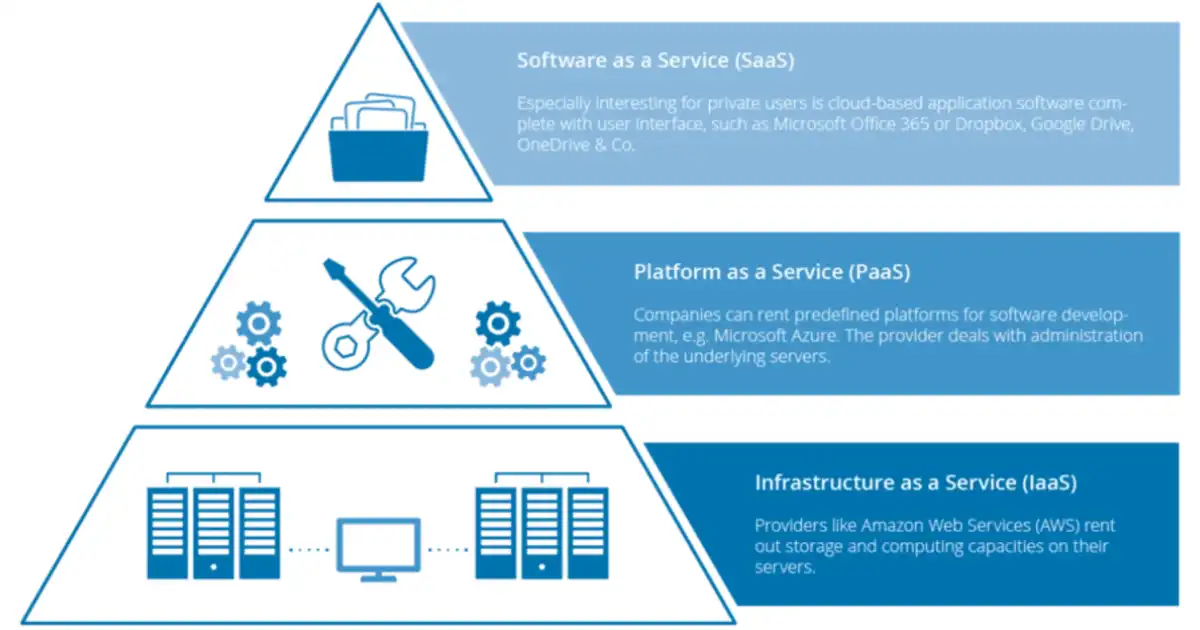
Security responsibilities change depending on the type of cloud service being used. The three main cloud service models are Infrastructure as a Service, Platform as a Service, and Software as a Service.
Infrastructure as a Service (IaaS)
In IaaS, the cloud provider manages physical infrastructure, networking, and virtualization. The customer controls operating systems, applications, data, and access management.
This means cloud customer security responsibilities are higher in IaaS. Customers must secure virtual machines, install patches, configure firewalls, and protect data.
Platform as a Service (PaaS)
In PaaS, the provider manages infrastructure and the platform layer, including operating systems and runtime environments. Customers focus on applications and data.
Here, cloud service provider security obligations increase, while customer responsibilities decrease slightly. However, customers still control application security and data protection.
Software as a Service (SaaS)
In SaaS, the provider manages almost everything, including applications. Customers mainly manage user access and data usage.
Even in SaaS, customers are responsible for strong passwords, user roles, and data governance. Security is shared, not transferred.
Cloud Service Provider Security Obligations
Cloud providers invest heavily in securing their platforms. Their responsibilities focus on protecting the foundation of the cloud environment.
Physical Data Center Security
Cloud providers secure data centers with strict physical controls. These include surveillance cameras, biometric access, security guards, and restricted entry zones.
This level of physical protection is difficult for most organizations to achieve on their own, which is a major benefit of cloud computing.
Infrastructure and Hardware Protection
Providers are responsible for securing servers, storage devices, and networking equipment. They ensure hardware is protected from tampering and failure.
They also handle hardware lifecycle management, including secure disposal of old equipment.
Network Security
Cloud providers protect the core network infrastructure from attacks. This includes protection against denial-of-service attacks and ensuring network isolation between customers.
They also provide secure connectivity options that customers can configure for additional protection.
Core Platform and Virtualization Security
Providers secure the hypervisor and core services that allow multiple customers to share the same physical resources safely.
This isolation ensures one customer cannot access another customer’s data or systems.
Cloud Customer Security Responsibilities
While cloud providers secure the foundation, customers are responsible for everything they build on top of it.
Identity and Access Management
Managing user access is one of the most critical cloud customer security responsibilities. Customers must create strong authentication policies, use multi-factor authentication, and assign permissions carefully.
Poor access management is one of the leading causes of cloud security breaches.
Data Protection and Encryption
Customers are responsible for protecting their data. This includes choosing encryption settings, managing encryption keys, and deciding who can access sensitive information.
Even if data is stored on a secure cloud platform, weak data controls can still lead to exposure.
Application Security
Customers must ensure that applications deployed in the cloud are secure. This includes writing secure code, patching vulnerabilities, and testing for weaknesses.
Cloud providers do not review or secure customer application logic.
Configuration and Monitoring
Misconfigured resources are a major risk in cloud environments. Customers must correctly configure storage, databases, and network settings.
Continuous monitoring helps detect suspicious activity early and reduce damage from attacks.
Customer vs Cloud Provider Security Roles Explained Simply
The easiest way to understand customer vs cloud provider security roles is to think of renting an apartment. The landlord secures the building structure, locks, and main utilities. The tenant secures personal belongings and decides who can enter the apartment.
Similarly, cloud providers secure the cloud infrastructure, while customers secure their data, applications, and users.
This clear division helps organizations know where to focus their security efforts.
Common Cloud Security Misunderstandings
Many cloud security issues come from misunderstandings rather than technical flaws.
One common myth is that cloud providers are responsible for all security. Another misconception is that cloud security is automatic and requires no effort from customers.
In reality, Cloud Security Basics require active involvement from both sides. Security tools provided by cloud platforms must be configured and managed correctly to be effective.
Shared Responsibility Model and Compliance
Compliance with regulations like data protection laws depends heavily on understanding the shared responsibility model.
Cloud providers may certify their infrastructure against industry standards. However, customers are responsible for using cloud services in a compliant way.
This includes data classification, access controls, and audit logging. Failing to meet these responsibilities can result in fines and legal issues.
Benefits of the Shared Responsibility Model
The shared responsibility model provides flexibility and scalability. Cloud providers focus on securing infrastructure at scale, while customers tailor security to their specific needs.
This approach allows organizations to innovate faster without sacrificing security. It also encourages customers to take ownership of their data and applications.
Challenges of Shared Cloud Security
Despite its benefits, the shared responsibility model can be challenging. Customers may lack cloud security expertise or underestimate their responsibilities.
Complex environments with multiple cloud services increase the risk of misconfiguration. This makes education and clear security policies essential.
Best Practices for Managing Cloud Security Responsibilities
Organizations should start by clearly defining roles and responsibilities. Training teams on Cloud Security Basics helps prevent mistakes.
Using automated security tools, enabling logging, and regularly reviewing configurations can greatly improve security posture.
Shared responsibility works best when customers actively manage their part of the model.
The Future of Cloud Security and Shared Responsibility
As cloud technology evolves, the shared responsibility model continues to adapt. Providers are offering more built-in security features, while customers are gaining better tools for visibility and control.
However, the core principle remains the same. Security is a shared effort that requires awareness, planning, and continuous improvement.
You Might Be Interested In
- How To Get Ai Dungeon Premium For Free?
- 10 Ai Applications Thriving On 6g’s Near-zero Latency
- What Are The Types Of Automatic Speech Recognition Systems?
- how does ai improve content quality and readability?
- How Does Ai Document Automation Work?
Conclusion
Understanding Cloud Security Basics and the shared responsibility model is no longer optional. It is essential for anyone using cloud services today. The shared responsibility model in cloud computing clearly defines who does what, reducing confusion and improving security outcomes.
Cloud providers handle physical infrastructure, networking, and core platform security. Customers manage data protection, access controls, and application security. When both sides fulfill their roles, cloud environments become more secure and reliable.
By recognizing cloud security responsibilities and respecting customer vs cloud provider security roles, organizations can confidently use cloud technology while protecting their data and users. A strong understanding of cloud service provider security obligations and cloud customer security responsibilities empowers better decisions and long-term success in the cloud.
FAQs about Cloud Security Basics
What is the shared responsibility model in cloud computing?
The shared responsibility model in cloud computing explains that security in the cloud is not handled by one party alone. Instead, it is divided between the cloud service provider and the customer. The provider is responsible for securing the underlying infrastructure such as physical data centers, hardware, networking, and core cloud services. This ensures that the foundation of the cloud environment is protected against physical threats, hardware failures, and large-scale attacks.
On the other hand, the customer is responsible for everything they place into the cloud. This includes managing data security, configuring cloud resources correctly, controlling user access, and securing applications. Understanding this model helps users clearly see where their responsibilities begin and prevents the common mistake of assuming the cloud provider handles all security aspects.
Why are cloud security responsibilities shared instead of fully managed by providers?
Cloud security responsibilities are shared because cloud providers cannot control how customers use their platforms. Customers decide what data to upload, who can access it, and how applications are built and configured. If providers were fully responsible for customer-side security, it would limit flexibility and raise privacy concerns, as providers would need deep access to customer data and systems.
Sharing responsibilities allows cloud platforms to remain flexible and scalable while giving customers full control over their digital assets. This balance ensures that providers focus on large-scale infrastructure protection, while customers apply security controls that match their specific business, compliance, and data protection needs.
How do customer vs cloud provider security roles differ in practice?
In practice, customer vs cloud provider security roles differ by layers of control. Cloud providers secure the physical environment, servers, storage hardware, networking, and virtualization technologies. They ensure that the cloud platform itself is stable, isolated, and protected from widespread threats that could affect multiple customers.
Customers, however, are responsible for securing what runs on top of this platform. This includes managing user identities, setting permissions, encrypting sensitive data, securing applications, and monitoring activity. Most cloud security incidents happen at this level, which is why understanding customer responsibilities is just as important as trusting the provider’s infrastructure security.
What happens if a customer ignores their cloud customer security responsibilities?
If a customer ignores their cloud customer security responsibilities, even the most secure cloud platform cannot prevent security incidents. Common issues like weak passwords, open storage access, or misconfigured networks can lead to data leaks and unauthorized access. These mistakes are often exploited quickly because cloud environments are always connected to the internet.
Beyond security breaches, ignoring responsibilities can result in legal and financial consequences. Regulatory violations, loss of customer trust, and service downtime can severely impact an organization. This is why actively managing cloud security settings and following best practices is critical for safe and reliable cloud usage.
Do cloud service provider security obligations change with different cloud services?
Yes, cloud service provider security obligations change depending on whether the service is Infrastructure as a Service, Platform as a Service, or Software as a Service. In Infrastructure as a Service, the provider secures the physical infrastructure, while the customer handles operating systems, applications, and data security. This gives customers more control but also more responsibility.
In Platform as a Service and Software as a Service, providers take on more security duties by managing operating systems, platforms, and sometimes applications. However, customers are never fully free from responsibility. They must still manage user access, data protection, and usage policies. Understanding these differences helps users apply the right level of security for each cloud service they use.
